vCvCISO Lite
Launching today
Enforcement. Your policy says it. Now it happens.
Every requirement in a company’s approved security policies becomes a standard with an owner, a schedule and a test. Graded against the company’s own numbers, run on schedule, and proven by evidence anyone can check.
New to compliance
Graded against your numbers. Every technical check reads the value in the company’s own clause. Change the policy and the grades follow.
Process controls that run themselves. Access reviews open on schedule, pull and seal live account lists, route each account to its manager, and close on sign-off.
No control left behind. The directory syncs from Okta, Entra ID, Google Workspace or BambooHR. A named backup takes over the day an owner leaves.
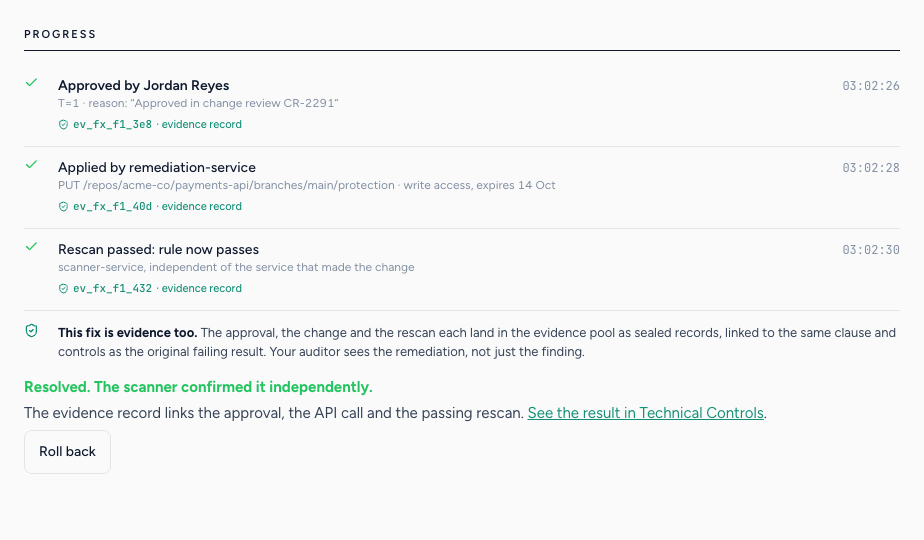
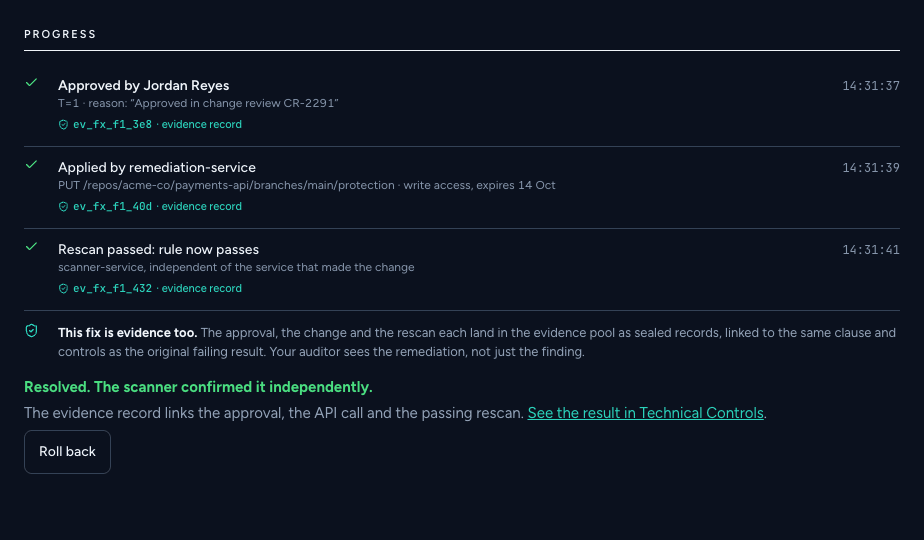
Done means a rescan passed. The service that applied a fix never marks it done; an independent rescan does, or the change is rolled back.
The essentials, done better
Standards, versioned like policies. AI drafts from the clause; a named person approves every version.
One list of fixes. Drift and missed process steps together. Engineering fixes go to Jira or Linear, with alerts in Slack or Teams.
Proof an auditor can check. Every approval, decision and rescan sealed and independently timestamped on the Evidence Graph.
Availability
Business and aboveIncluded
Fixes that apply themselvesEnterprise
Ships alongside rebuilt Connections and Security Scanning. No separate SKU.
Fast facts
AvailableToday, generally available
ForGrowing companies without a full-time CISO
In the appEnforcement → Posture, Standards, Fixes
To startApproved policies and a connected identity provider
Learn morevcisolite.com/enforcement
“A policy nobody runs is a liability with a signature on it. What companies can’t show is that the policy is followed on an ordinary Tuesday, when no audit is coming.”Yolonda Smith, founder, vCISO Lite