About vCISO Lite
The elements you can build on.
vCISO Lite is the compliance and cyber risk platform for growing companies. It was built to remove security as an obstacle to solving business problems, not to add another dashboard for security people to admire. It's what a working CISO builds when she's tired of watching small companies get shut out of the fundamentals enterprises take for granted, and priced so a thirty-person company can actually operate it from day one.
Why we built this
Small companies aren't underprepared. They're underserved.
Our mission
To put compliance, risk quantification, diligence, and experienced leadership within reach of every company with business to defend — not just the ones with enterprise budgets.
Enterprise buyers now expect every vendor, regardless of size, to demonstrate the same security posture a Fortune 500 supplier would. Compliance frameworks. Third-party risk assessments. Quantified cyber exposure. Board-ready reporting. The bar keeps rising and enforcement moves earlier: procurement doesn't wait for the security incident anymore. They price it in at contract negotiation. And they walk when the answers don't come back fast enough.
54%
of companies lose deals to security questionnaires
Fifty-four percent. More than half of every enterprise deal a growing company has fought to get in front of. And it's the visible tip of a longer pattern: each security questionnaire takes ten to forty hours to complete manually, and 86% of B2B purchases stall somewhere in the buying cycle. A late security review is one of the most reliable stall points. Security stopped being a “we'll deal with it in due diligence” problem years ago. It's a sales-motion problem now, and it decides deals before anyone at the target company is even in the room.
The received wisdom is that a fractional CISO plus enterprise GRC tooling is “the SMB solution.” In practice, that's $250,000 a year for something a thirty-person company can't afford, hasn't budgeted for, and doesn't have the internal capacity to operationalize. Meanwhile the incidents don't wait for you to be ready.
80%
of SMBs experienced at least one cyberattack in 2025
Eight out of ten. Not “one in ten if you're unlucky” — the baseline. When one of those attacks lands, the average total cost for an SMB runs around $254,000. And 40% of the SMBs hit say an incident that size would end the business outright. The threat isn't hypothetical, and the “we'll figure it out if it happens” playbook is a bet against a loaded coin — one where the downside is not existing anymore.
On the deal side of the same equation (capital raises, acquisitions, exits), cyber issues have quietly become one of the most reliable line items to devalue a transaction. Or kill it entirely.
7–12%
average deal-valuation reduction when cyber issues surface in diligence
Seven to twelve percent off the top of your valuation, discovered during diligence, before the term sheet is signed. And that's the number for the deals that still close. On the ones that don't: 73% of dealmakers say they walk from a deal with undisclosed cyber issues, and 80% report finding cyber issues in at least a quarter of the M&A targets they diligence. The “we'll clean it up after we close” strategy is over. Buyers do the math before you get to the term sheet, and they price it into the offer or leave.
Which brings it back to the people who need this most. The founder closing the round who told the diligence lawyer she'll have a SOC 2 by December. The CTO whose enterprise deal is stalling on the security questionnaire. The CFO trying to model what a breach would actually cost the business. The deal partner sizing an acquisition target whose cyber posture is a black box. None of them are security people. All of them need a security posture that unblocks the next business decision. That's what vCISO Lite is for.
What we stand for
Transparency
Every tier and price is published. You shouldn't have to book a sales call just to find out whether we fit your budget. We use our own product as part of our own compliance journey, and we document that process publicly. We're clear about how and where we use AI, and about the measures we take to make sure its outputs stay accurate, consistent, and trustworthy.
Integrity
We hold ourselves accountable to the truth. That matters especially when you're making business decisions on the basis of our platform's outputs. Every output the platform produces is independently verifiable — by your auditor, your forensics team, or you. Trust shouldn't require faith; it should require evidence.
How to work with us
The whole program. Or the one thing you need.
We're organized so you can work with us in whichever way fits the problem in front of you. Subscribe to vCISO Lite and run it yourself: the whole program, end-to-end, at a price a growing company can actually operate. Or engage Other20 Advisory for a specific problem, like a diligence engagement, a security questionnaire response, or an audit, and pay only for the piece you need. Both share the same evidence graph underneath, so anything humans deliver stays visible in the platform and vice versa.
vCISO Lite
The platform. Subscribe, run it yourself, cover the whole program end-to-end: compliance across 250+ frameworks, cyber risk quantification in dollars, third-party and vendor risk management, M&A cyber diligence, governed agentic operations, board-ready reporting. From $299/month.
Other20 Advisory
Expert-led engagements for specific problems. A single diligence. A security questionnaire response. Audit support. Enterprise-deal security response. Pay for the piece you need, delivered by humans who use the platform themselves.
Behind the curtain
Every surface is a metal. Together, they're a program.
Who leads this
Founder & CEO — Yolonda Smith.
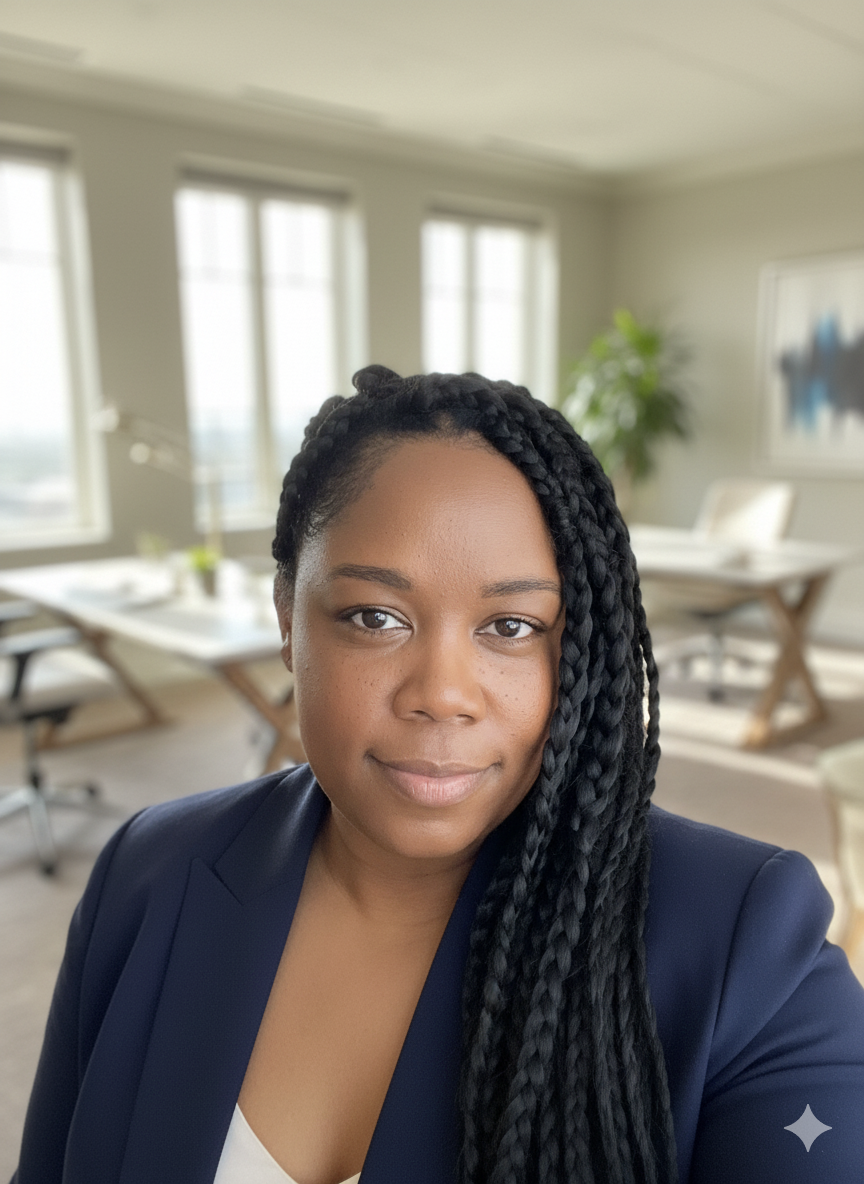
CISSP · CISM · GCIH · GSEC · CISO Certification, Carnegie Mellon Heinz College · BS Computer Science, University of Notre Dame · MS Information Assurance, University of Maryland · U.S. Air Force veteran
I've spent twenty years running security programs from every angle: first as a Cyberspace Operations Officer in the U.S. Air Force, then at Pwnie Express, then Target, then Head of Cybersecurity at sweetgreen and Grubhub. I've been the IT Director whose security portfolio was an additional duty, with no headcount and no budget but all of the responsibility to “make sure nothing bad happens.” I've scaled programs from nothing all the way through IPO. I've led internal M&A diligence and felt the pressure of “just say yes, we don't have time for security to be the hold-up.”
I know how frustrating security can be. I've been the security person in every one of those rooms. I also know the look on the executive's face wondering “why do I have to care about this,” “is this really that important,” “is this all just scare tactics?” And the honest answer is: a lot of security isscare tactics, because it's an impossible position. You can't actually demonstrate a security ROI that makes sense to the business — but they know you're needed for some reason — and when you can't quantify the value, all you're left with is quantifying the fear.
Long before vCISO Lite, I was talking publicly about how to bridge the communication gap between security people and everyone else, first at DevOpsDays, then TEDx, Grace Hopper, and The Diana Initiative. The books came later, both in 2026, and a different kind of work. Someone Else's Debt is a framework for quantifying cyber risk during an M&A deal. Someone Else's Breach is a playbook for how to conduct incident response when it's your vendor that got breached. The methodologies in both are now foundational IP inside vCISO Lite. If you're using the platform, you're getting quantitative cyber diligence and vendor incident response built in.
That's why I built vCISO Lite. It's the bridge between the beleaguered security person who's been trying to explain why any of this matters, and the C-level who's tired of hearing the answers sound like scare tactics. Explore the platform →
vCISO Lite is part of Argon Holdings, headquartered and operated in Atlanta, Georgia.