Field note · Incident study
ARTEX Isn't a New Weapon. It's One That Upgrades Itself.
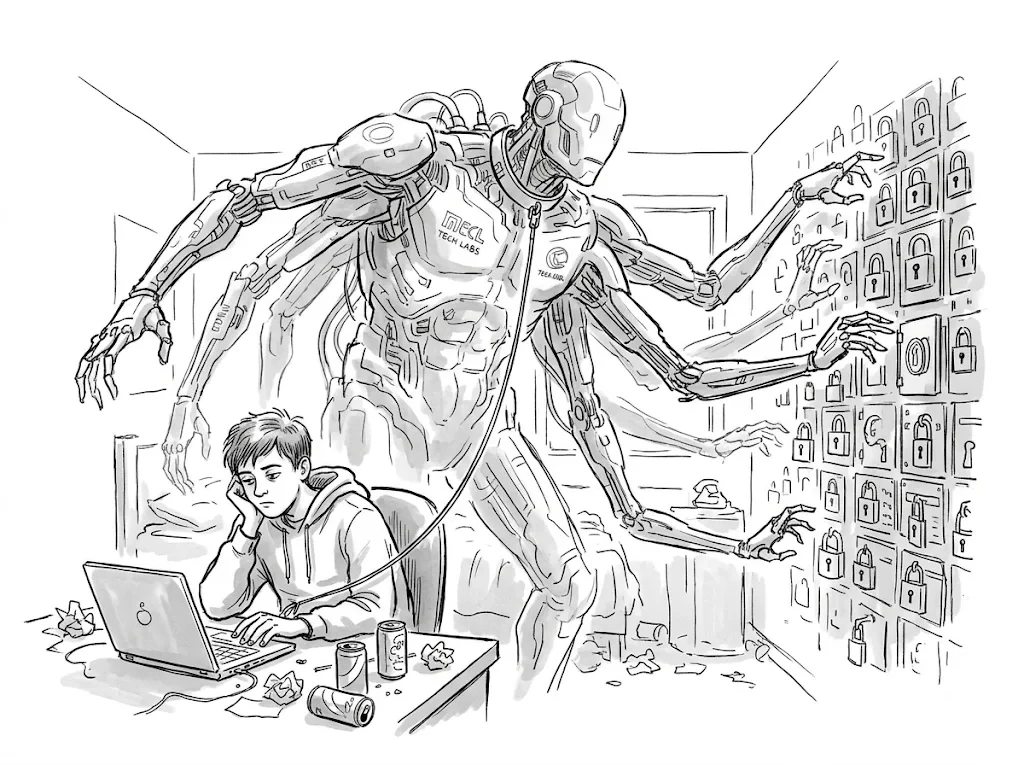
In early October 2026, investigators at CrowdStrike found a server someone had left open to the internet, and on it the working papers of a theft: the session logs and configuration of ARTEX, an AI attack framework, laid over the records of about 67,000 people taken from seven South Korean financial firms — income, loans, the kind of detail a bank holds on you. The opening the operator used was nothing special: a customer lookup that returned records by ID without checking who was asking. A script could have walked it in 2005.
Which is the puzzle worth sitting with. Scripted attacks are thirty years old. Agentic AI pentest tools already exist — we ship one. Ungoverned offensive tools leak onto GitHub constantly and nobody flinches. So why did this one draw an FBI flash alert, and why did its own author take it down and go closed-source within days? The honest answer isn’t that ARTEX can do something new. It’s that, for the first time in a tool anyone could download, the attacker’s capability scales with frontier AI instead of with people — and that changes the category.
The autopsy
What the attackers’ own exposed server showed — and what it didn’t.
The server they forgot to lock
The break came because the operators made their victims’ mistake: they left a server open to the internet. CrowdStrike found it at 38.244.50.120— an open directory holding the campaign’s session logs, ARTEX configuration, and the agents’ memory files. Nobody intercepted this attack in flight. Investigators read the attacker’s own working papers after the fact.
Rented brains, borrowed plumbing
Those files showed the shape of the operation. DeepSeek models drove the scanning, reached not directly but through an LLM reseller, xcai[.]pro, and a rotating set of nine proxy addresses meant to keep the model traffic from pointing home. The intelligence was rented by the hour; the only part the operators built themselves was the anonymization.
The way in — what the data implies
No vendor has published the exact flaw, so this step is inference — but the shape of the theft and the defensive guidance that followed (Zscaler and others) point the same way: a customer-facing lookup that returned records by ID with no authorization check and no rate limit. An insecure direct object reference, the plainest entry on OWASP’s list, older than most banks’ websites. The data left the way it leaves when that’s true — one ID after the next, at machine pace.
The haul
About 67,000 people’s records across seven firms — income, loans, the sensitive detail a lender holds — in roughly a week. The firms remain unnamed, and South Korea’s regulators have separately described a larger tally, on the order of 100,000 records across 16 institutions, that may be a different count.
Read it back and the operators look unremarkable, because they were. They rented their intelligence, botched their own security badly enough to be caught by it, and walked in through a flaw a tester could have named in 2010. That is the unsettling part, not a reassuring one. Nothing in the method was new or hard, and the capability wasn’t even theirs — it was rented by the hour, and it will be cheaper and better next quarter.
So the question isn’t how these particular operators got in. It’s why a tool that only automates ordinary flaws drew a response usually saved for something genuinely new.
Why this, and not mimikatz
Ungoverned offensive tools are not new. Credential stealers, exploit frameworks and cracked command-and-control kits have circulated openly for two decades, and none of them pulled an FBI flash or a panicked takedown by their own author. “The guardrails came off a tool” can’t be the reason for this reaction, because that describes half of GitHub.
What ARTEX has that a leaked tool doesn’t is that its power is not fixed. mimikatz is as capable today as the day it shipped. ARTEX is model-agnostic plumbing, so its ceiling is set by whatever AI you point it at — and that ceiling rises on its own. Three properties follow, and no prior offensive tool had them together:
It compounds, for free.Every time any lab ships a more capable model, every copy of ARTEX gets better at reconnaissance, at reading an unexpected response, at chaining the next step — with zero effort from whoever holds it. The threat improves on someone else’s research budget, on someone else’s release schedule, and there is nothing to patch.
Its safety ceiling is the weakest model on the market, not the best. An attacker routes to whichever model refuses least. The FBI notes that DeepSeek’s cheaper models dominated ARTEX usage precisely because they don’t push back when a task is framed as penetration testing. So no single provider’s guardrails decide the outcome; the floor is set by the least-cautious frontier model available, and there is always one.
It adapts faster than defense can fingerprint. Signature- and indicator-based defense assumes an attack is static enough to catalog. An agent rewrites its approach per target and per response, and the FBI’s own indicators section half-concedes the problem — the infrastructure is ephemeral, the advice is to corroborate against live telemetry rather than block a list. You can’t blocklist something that doesn’t repeat itself.
That is the line you can’t uncross. You can pull a tool off GitHub; its author did. You cannot pull “frontier models can be aimed at a target,” and you cannot recall a capability that gets stronger every month without the attacker lifting a finger. ARTEX set off the alarm because it was the first undeniable proof that this is here, works, is free, and compounds — and because four unrelated crews, state and criminal, picked it up within weeks of each other. People don’t do that over hype.
Two honest hedges, so this doesn’t tip into breathlessness. The analysts who have actually held ARTEX’s logs report that a great deal of the work still looks like ordinary scripting, and the “fully autonomous” story runs ahead of the proof. And it was mostly Chinese models, not the US frontier labs, doing the heavy lifting. The alarm is about the trajectory this proves out as much as the damage done so far — but a trajectory this clear is itself the thing worth planning around.
The symmetry problem
Here is what that trajectory means for a company your size, and it runs straight through our own product. The capability in ARTEX is the same one a defender uses: our red-team service points agentic tooling at a customer’s systems to find what’s weak, under a defined scope and their consent. ARTEX is that engine with the scope deleted and the keys handed out — the same work, aimed at anyone, by anyone. Offense and defense have drawn even on capability, and offense got free distribution.
Two old assumptions die in that symmetry. The first is “we’re too small or too boring to be worth a skilled attacker’s week.” One operator ran ARTEX against 200-plus organizations in ten days; being unremarkable is no longer cover, because nobody has to spend a week on you. The second is quieter and worse: a security posture is not a fixed thing anymore. If the attacker’s capability rises with every model release, then the gap between what you tested for last year and what can be thrown at you today widens on its own, for free, while you do nothing. Last year’s clean pentest is already stale.
What vCISO Lite would and wouldn’t have changed
We’re a compliance and posture platform, not a 24/7 detection service, and we can’t slow the trajectory. The honest split.
When ARTEX chained two unknown Zammad flaws to root on a Dutch research team’s network, no checklist would have closed a hole the vendor didn’t know about. Patching helps after the fix exists, not before.
Spotting an intrusion that reaches privileged access in under three hours is the job of monitoring and response — your MDR or SOC. We don’t watch your logs in real time, and we’d be lying if we said we did.
We scan and test the systems you connect; we don’t discover a shadow endpoint nobody told us about. Keeping the inventory honest is still your job — we make it a standing question, not a magic trick.
Finding an IDOR isn’t the differentiator — plenty of tools do that. What comes next is. Our red-team service, powered by Red Claw, surfaces the flaw and then ties it to the business function behind that endpoint and the revenue at risk — so a lone IDOR reads as “the customer-servicing function can be walked, record by record,” not one more line on a CVSS list. That is the altitude this note opened at: the attack was ordinary; what it threatens isn’t.
The dependency map names the business functions tied to each system and the single points of failure among them. So one walked endpoint isn’t an isolated bug to be triaged by severity — it’s a visible slice of the business, ranked against everything else by what it would actually cost you.
Because the attacker upgrades every model release, an annual test is stale by spring. The same red-team service runs on a cadence against your own systems — the only pace that keeps up with a threat that keeps up with the models.
Our read
Three positions, in order of confidence.
One. The capability isn’t new; its trajectory is. Scripts, exploit kits and even agentic pentest tools all predate ARTEX. What’s new in a tool anyone can hold is that its power scales with frontier AI — so it compounds for free and routes around any one lab’s guardrails. That, not a novel exploit, is why the FBI issued a flash and the author pulled his own project.
Two. Offense and defense are the same engine now, and offense got free distribution. The tool pointed at those Korean banks is the one a defender runs with consent and a scope. Strip those and open-source it and you get ARTEX. “Too small to target” is gone — one operator, 200 organizations, ten days.
Three. The only defense that keeps pace is a continuous one. A posture that was clean last year decays on its own as the models improve. Inventory your edges, fix the boring web flaws, and test them on a cadence rather than once a year. It is unglamorous, it is exactly the work lean teams skip for lack of time, and it is the one response that scales the way the threat does. We hold this most firmly, because it doesn’t depend on the attacker’s intent or on how autonomous the tool really is. It depends only on the models getting better, and they will.
Primary sources
- SOC Prime — ARTEX AI-driven campaign hits seven South Korean financial firms (Oct 16, 2026; CrowdStrike Oct 7 research)
- FBI — FLASH-20261113-001, Threat Overview of ARTEX Autonomous Penetration Testing Framework (Nov 13, 2026)
- SentinelOne — ARTEX Unmasked: cross-actor use by state and criminal groups (Vapor Panda, Storm-0940, Storm-3358, TAG-217)
- The developer closes ARTEX and goes closed-source after the South Korean bank attack (Oct 8, 2026)
- Huntress — on the limits of the autonomy claims (“a lot looks like ordinary scripts”)
Reporting on ARTEX is young and the vendor accounts don’t fully agree — on victim counts, on how autonomous the tool truly is, on exact entry flaws. Where sources conflict, this note names the source, and its argument is built to hold whether or not a model was fully in the loop.